Enterprise Risk Management (ERM) Consulting and Training in Singapore: Build Resilience, Reduce Crisis Risk
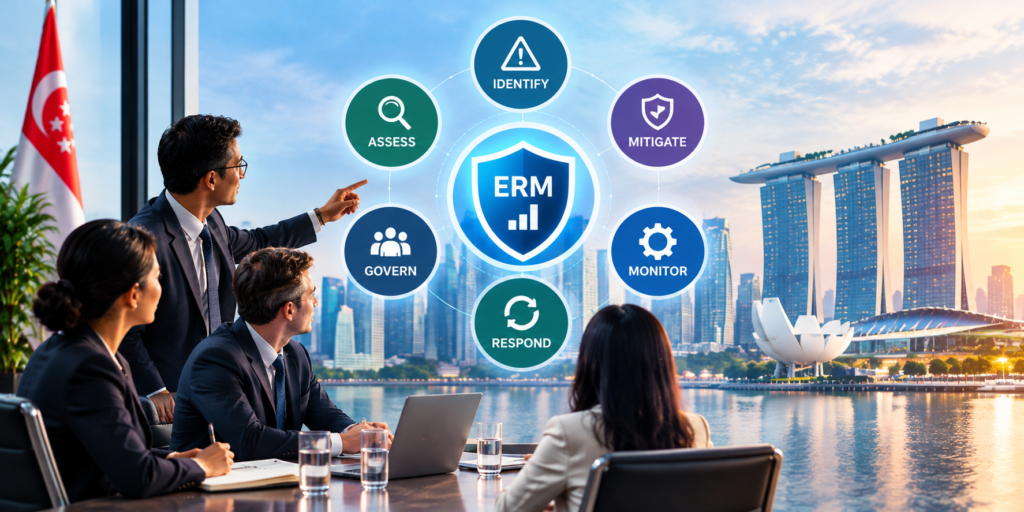
Enterprise Risk Management (ERM) isn’t just about compliance or risk reporting. It’s about building organizational resilience—identifying and controlling risks before they become crises. This guide explains what modern ERM is, why Singapore companies need it, what consulting and training covers, and how to choose the right partner to build ERM maturity in your organization. The Business Case: Why ERM Matters Now The reality of modern business risk: Singapore companies face a complex risk landscape: The problem: Most companies manage risks in silos: The gaps: The solution: Enterprise Risk Management (ERM) provides a framework to: The outcome: Companies with mature ERM: What Is Enterprise Risk Management (ERM)? The definition: Enterprise Risk Management is a structured, board-approved process for identifying, assessing, controlling, monitoring, and reporting on risks across the entire organization—aligned with the company’s strategy and risk appetite. Key elements: Why it’s different from traditional risk management: Traditional Risk Management Enterprise Risk Management (ERM) Manages risks in silos (finance, IT, ops) Integrated view across the organization Reactive (responds to problems) Proactive (identifies risks before crisis) Focuses on compliance and reporting Focuses on strategy, performance, and resilience Reports to individual committees Reports to board and executives Doesn’t align with strategy Aligned with business strategy and risk appetite Real example: A Singapore bank’s traditional approach: A crypto exchange hacks the bank’s systems. Under traditional silos: With ERM: Why Singapore Companies Need ERM Now Five drivers: 1. Regulatory Expectations Have Increased MAS (Monetary Authority of Singapore): SGX (Singapore Exchange): PDPA (Personal Data Protection Act): Sector-specific regulators: 2. Business Complexity Has Grown 3. Crises Are More Costly and Public 4. Investors and Partners Scrutinize Risk Management 5. Competitive Advantage Through Resilience What Enterprise Risk Management Consulting Covers When you engage an ERM consultant, here’s what you’re getting: 1. Risk Maturity Assessment What it covers: Deliverables: Why it matters: You can’t improve what you don’t understand. A maturity assessment gives you a clear picture of current state and direction for improvement. 2. Risk Appetite and Tolerance Setting What it covers: Deliverables: Why it matters: Without clear risk appetite, executives don’t know how much risk to take. They either take too much (leading to crises) or too little (missing opportunities). A defined risk appetite aligns decision-making. Real example: A manufacturing company’s board defines risk appetite: This guides executive decisions. When a salesperson wants to do business with a new supplier, they check against risk appetite. If the supplier can’t meet standards, it’s an automatic no. 3. Enterprise-Wide Risk Identification What it covers: Methodology: Deliverables: Why it matters: Most companies don’t know all the risks they face. They discover them when crises happen. A systematic risk identification ensures the board knows what could hurt the company. Real example: A Singapore tech company’s risk identification workshop uncovers: Before this workshop, executives knew about some of these. The workshop ensures the board sees the complete picture. 4. Risk Assessment and Prioritization What it covers: Deliverables: Why it matters: Not all risks are equally important. Assessment and prioritization focus the organization on the most significant risks and how to control them. Real example: A manufacturing company’s risk heat map shows: The company focuses resources on top-left and top-right risks. Bottom-left is monitored but not heavily invested. Bottom-right is monitored but minimal effort. 5. Risk Control and Mitigation Strategy What it covers: Control framework: Deliverables: Why it matters: Identifying risks is step one. Controlling them is the real work. A clear control strategy ensures you’re spending capital on the highest-impact mitigations. Real example: A Singapore bank’s cyber risk control strategy: When a cyber attack occurs, these controls minimize impact and accelerate response. 6. Risk Governance and Organization What it covers: Governance model options: Deliverables: Why it matters: If no one is accountable for risk, risks aren’t managed. Clear governance ensures risk oversight is consistent and connected to the board. 7. Risk Monitoring and Reporting What it covers: KRIs (Key Risk Indicators): Reporting framework: Deliverables: Why it matters: Risks change. What’s high-risk today might be low-risk tomorrow (or vice versa). Continuous monitoring and reporting keep the board and management current and enable early response. 8. Crisis Management and Business Continuity What it covers: Deliverables: Why it matters: Even with good controls, things go wrong. A crisis management plan ensures you respond quickly and minimize damage. 9. Risk Culture and Change Management What it covers: Culture elements: Deliverables: Why it matters: ERM frameworks don’t work without a supporting culture. If executives see risk management as a checkbox, it fails when real crises hit. What Enterprise Risk Management Training Covers ERM training complements consulting—it builds organizational capability so risk management is sustained over time. 1. Executive Leadership on ERM (1–2 days) Who it’s for: What it covers: Outcome: 2. Board-Level Risk Governance Training (2–3 days) Who it’s for: What it covers: Outcome: 3. Risk Management Program (3–5 days) Who it’s for: What it covers: Outcome: 4. Specialized Risk Tracks Examples: Cyber and Technology Risk Management (2–3 days) Operational Risk Management (2–3 days) Financial Risk Management (2–3 days) Compliance and Regulatory Risk (1–2 days) Climate and ESG Risk (1–2 days) The ERM Consulting and Training Process How a typical ERM engagement unfolds: Phase 1: Discovery and Assessment (Weeks 1–4) Phase 2: Strategic Planning (Weeks 5–8) Phase 3: Risk Identification and Assessment (Weeks 9–16) Phase 4: Control Design and Implementation (Weeks 17–28) Phase 5: Training and Rollout (Weeks 29–36) Phase 6: Embedding and Sustaining (Weeks 37–52) How to Choose an ERM Consulting and Training Partner What to look for: ✓ Deep Singapore and ASEAN Experience ✓ Proven ERM Frameworks ✓ C-Suite and Board Experience ✓ Practical Implementation Focus ✓ Blended Approach: Consulting + Training ✓ Sector Expertise (If Relevant) ✓ Flexibility and Customization ERM Implementation Roadmap: 12-Month Plan What a typical 12-month ERM implementation looks like: Months 1–2: Foundation Months 3–4: Strategy and Governance Months 5–7: Risk Identification and Assessment Months 8–9: Control Design and Monitoring Months 10–11: Training and Communication Month 12: Embedding and Review Year 2+: Sustaining and Improving The ROI: What You’ll Get From ERM Consulting and Training Direct benefits: Indirect benefits: Quantifiable outcomes: ERM Consulting and Training