Enterprise Risk Management (ERM) Consulting and Training in Singapore: Build Resilience, Reduce Crisis Risk
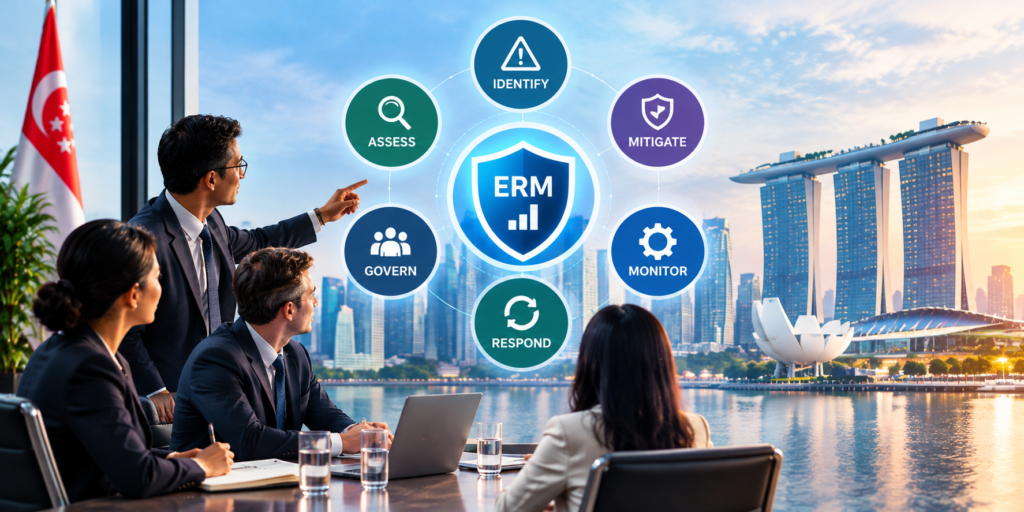
Enterprise Risk Management (ERM) isn’t just about compliance or risk reporting. It’s about building organizational resilience—identifying and controlling risks before they become crises. This guide explains what modern ERM is, why Singapore companies need it, what consulting and training covers, and how to choose the right partner to build ERM maturity in your organization. The Business Case: Why ERM Matters Now The reality of modern business risk: Singapore companies face a complex risk landscape: The problem: Most companies manage risks in silos: The gaps: The solution: Enterprise Risk Management (ERM) provides a framework to: The outcome: Companies with mature ERM: What Is Enterprise Risk Management (ERM)? The definition: Enterprise Risk Management is a structured, board-approved process for identifying, assessing, controlling, monitoring, and reporting on risks across the entire organization—aligned with the company’s strategy and risk appetite. Key elements: Why it’s different from traditional risk management: Traditional Risk Management Enterprise Risk Management (ERM) Manages risks in silos (finance, IT, ops) Integrated view across the organization Reactive (responds to problems) Proactive (identifies risks before crisis) Focuses on compliance and reporting Focuses on strategy, performance, and resilience Reports to individual committees Reports to board and executives Doesn’t align with strategy Aligned with business strategy and risk appetite Real example: A Singapore bank’s traditional approach: A crypto exchange hacks the bank’s systems. Under traditional silos: With ERM: Why Singapore Companies Need ERM Now Five drivers: 1. Regulatory Expectations Have Increased MAS (Monetary Authority of Singapore): SGX (Singapore Exchange): PDPA (Personal Data Protection Act): Sector-specific regulators: 2. Business Complexity Has Grown 3. Crises Are More Costly and Public 4. Investors and Partners Scrutinize Risk Management 5. Competitive Advantage Through Resilience What Enterprise Risk Management Consulting Covers When you engage an ERM consultant, here’s what you’re getting: 1. Risk Maturity Assessment What it covers: Deliverables: Why it matters: You can’t improve what you don’t understand. A maturity assessment gives you a clear picture of current state and direction for improvement. 2. Risk Appetite and Tolerance Setting What it covers: Deliverables: Why it matters: Without clear risk appetite, executives don’t know how much risk to take. They either take too much (leading to crises) or too little (missing opportunities). A defined risk appetite aligns decision-making. Real example: A manufacturing company’s board defines risk appetite: This guides executive decisions. When a salesperson wants to do business with a new supplier, they check against risk appetite. If the supplier can’t meet standards, it’s an automatic no. 3. Enterprise-Wide Risk Identification What it covers: Methodology: Deliverables: Why it matters: Most companies don’t know all the risks they face. They discover them when crises happen. A systematic risk identification ensures the board knows what could hurt the company. Real example: A Singapore tech company’s risk identification workshop uncovers: Before this workshop, executives knew about some of these. The workshop ensures the board sees the complete picture. 4. Risk Assessment and Prioritization What it covers: Deliverables: Why it matters: Not all risks are equally important. Assessment and prioritization focus the organization on the most significant risks and how to control them. Real example: A manufacturing company’s risk heat map shows: The company focuses resources on top-left and top-right risks. Bottom-left is monitored but not heavily invested. Bottom-right is monitored but minimal effort. 5. Risk Control and Mitigation Strategy What it covers: Control framework: Deliverables: Why it matters: Identifying risks is step one. Controlling them is the real work. A clear control strategy ensures you’re spending capital on the highest-impact mitigations. Real example: A Singapore bank’s cyber risk control strategy: When a cyber attack occurs, these controls minimize impact and accelerate response. 6. Risk Governance and Organization What it covers: Governance model options: Deliverables: Why it matters: If no one is accountable for risk, risks aren’t managed. Clear governance ensures risk oversight is consistent and connected to the board. 7. Risk Monitoring and Reporting What it covers: KRIs (Key Risk Indicators): Reporting framework: Deliverables: Why it matters: Risks change. What’s high-risk today might be low-risk tomorrow (or vice versa). Continuous monitoring and reporting keep the board and management current and enable early response. 8. Crisis Management and Business Continuity What it covers: Deliverables: Why it matters: Even with good controls, things go wrong. A crisis management plan ensures you respond quickly and minimize damage. 9. Risk Culture and Change Management What it covers: Culture elements: Deliverables: Why it matters: ERM frameworks don’t work without a supporting culture. If executives see risk management as a checkbox, it fails when real crises hit. What Enterprise Risk Management Training Covers ERM training complements consulting—it builds organizational capability so risk management is sustained over time. 1. Executive Leadership on ERM (1–2 days) Who it’s for: What it covers: Outcome: 2. Board-Level Risk Governance Training (2–3 days) Who it’s for: What it covers: Outcome: 3. Risk Management Program (3–5 days) Who it’s for: What it covers: Outcome: 4. Specialized Risk Tracks Examples: Cyber and Technology Risk Management (2–3 days) Operational Risk Management (2–3 days) Financial Risk Management (2–3 days) Compliance and Regulatory Risk (1–2 days) Climate and ESG Risk (1–2 days) The ERM Consulting and Training Process How a typical ERM engagement unfolds: Phase 1: Discovery and Assessment (Weeks 1–4) Phase 2: Strategic Planning (Weeks 5–8) Phase 3: Risk Identification and Assessment (Weeks 9–16) Phase 4: Control Design and Implementation (Weeks 17–28) Phase 5: Training and Rollout (Weeks 29–36) Phase 6: Embedding and Sustaining (Weeks 37–52) How to Choose an ERM Consulting and Training Partner What to look for: ✓ Deep Singapore and ASEAN Experience ✓ Proven ERM Frameworks ✓ C-Suite and Board Experience ✓ Practical Implementation Focus ✓ Blended Approach: Consulting + Training ✓ Sector Expertise (If Relevant) ✓ Flexibility and Customization ERM Implementation Roadmap: 12-Month Plan What a typical 12-month ERM implementation looks like: Months 1–2: Foundation Months 3–4: Strategy and Governance Months 5–7: Risk Identification and Assessment Months 8–9: Control Design and Monitoring Months 10–11: Training and Communication Month 12: Embedding and Review Year 2+: Sustaining and Improving The ROI: What You’ll Get From ERM Consulting and Training Direct benefits: Indirect benefits: Quantifiable outcomes: ERM Consulting and Training
Enterprise Risk Management Singapore: A Comprehensive Guide for Modern Organizations
Why Enterprise Risk Management Matters in Singapore Enterprise Risk Management (ERM) has become a cornerstone of strategic business operations for organizations across Singapore. In an increasingly complex global business environment, where regulatory requirements intensify and market volatility accelerates, enterprise risk management Singapore represents a critical discipline for executives, boards, and risk managers seeking to protect organizational assets and drive sustainable growth. Singapore’s status as a leading global financial center demands that organizations implement sophisticated risk management frameworks. Whether facing operational disruptions, cybersecurity threats, regulatory changes, or market volatility, an effective enterprise risk management strategy provides the visibility and control necessary to navigate uncertainty while capturing opportunities. Understanding Enterprise Risk Management: Definitions and Core Principles Enterprise Risk Management is a comprehensive, integrated approach to identifying, analyzing, and responding to risks that affect organizational objectives across all business units and functions. Unlike traditional risk management that operates in silos, ERM takes a holistic view of risk across the entire enterprise. The COSO ERM Framework, widely adopted in Singapore, defines enterprise risk management as a process designed to identify potential events that may affect the entity and manage risks to be within the entity’s risk appetite, providing reasonable assurance regarding achievement of objectives. Key Components of Enterprise Risk Management in Singapore 1. Risk Identification Risk identification is the foundational step in enterprise risk management Singapore. Organizations must systematically identify potential risks across operational, financial, strategic, compliance, and reputational dimensions. This involves analyzing business processes, interviewing stakeholders, conducting scenario analysis, and reviewing industry benchmarks. For Singapore-based organizations, risk identification must account for market-specific factors including regulatory changes from the Monetary Authority of Singapore (MAS), evolving Personal Data Protection Act (PDPA) requirements, geopolitical considerations, and sector-specific vulnerabilities. 2. Risk Assessment and Analysis Risk assessment evaluates the probability and potential impact of identified risks. Enterprise risk management in Singapore employs both quantitative and qualitative assessment methodologies to prioritize risks by severity and develop appropriate mitigation strategies. Assessment frameworks typically evaluate risks across multiple dimensions including financial impact, operational disruption, regulatory exposure, and reputational consequences. 3. Risk Response and Mitigation Once risks are identified and assessed, organizations develop targeted response strategies. Enterprise risk management Singapore typically employs four primary response approaches: risk avoidance (eliminating the risk), risk reduction (implementing controls to mitigate impact), risk transfer (through insurance or contracts), and risk acceptance (tolerating risks within acceptable thresholds). The choice of response depends on the organization’s risk appetite and strategic priorities. 4. Risk Monitoring and Reporting Effective enterprise risk management Singapore requires continuous monitoring of identified risks and the effectiveness of implemented controls. Organizations establish key risk indicators (KRIs), conduct regular risk assessments, and provide transparent reporting to the board and executive management. This enables proactive identification of emerging risks and timely adjustment of mitigation strategies. Types of Enterprise Risks Affecting Singapore Organizations Enterprise Risk Management and Singapore Regulatory Requirements Singapore’s regulatory landscape increasingly mandates formal enterprise risk management frameworks. Financial institutions are subject to MAS’s risk management guidelines, while all organizations must comply with corporate governance standards and the Personal Data Protection Act. The Singapore Code of Corporate Governance emphasizes risk management as a board responsibility, requiring directors to oversee ERM effectiveness and report to shareholders. Organizations implementing enterprise risk management Singapore align with international best practices while satisfying local regulatory expectations, positioning themselves as governance-conscious entities attractive to investors, partners, and regulators. Benefits of Enterprise Risk Management for Singapore Organizations: Frequently Asked Questions: Enterprise Risk Management Singapore Q1: What’s the difference between risk management and enterprise risk management? Traditional risk management typically focuses on specific risk areas in isolation, such as operational risks or financial risks. Enterprise Risk Management (ERM), by contrast, takes an integrated, organization-wide approach that examines how risks interact and affect overall business objectives. ERM aligns risk management with strategic planning and ensures consistent risk governance across all business units. Q2: Is enterprise risk management mandatory for Singapore organizations? While formal ERM is mandatory for financial institutions regulated by MAS, it’s recommended best practice for all organizations. The Singapore Code of Corporate Governance requires boards to oversee risk management systems. Many organizations adopt formal ERM to meet stakeholder expectations, improve governance, and demonstrate operational maturity. Q3: How much does implementing enterprise risk management cost? ERM implementation costs vary based on organization size, complexity, and existing risk management infrastructure. Initial implementation may require investment in frameworks, tools, training, and potentially external consultants. However, these upfront costs are typically offset by reduced losses from prevented incidents, avoided penalties, and improved operational efficiency. Q4: What are key risk indicators (KRIs) in enterprise risk management? Key Risk Indicators are metrics that provide early warning signals of emerging risks. Examples include cybersecurity incident frequency, regulatory violation counts, supply chain concentration ratios, or customer complaint trends. KRIs enable organizations to detect deteriorating conditions before they manifest as actual losses, supporting proactive risk management. Q5: Which frameworks guide enterprise risk management in Singapore? The primary frameworks include the COSO Enterprise Risk Management Framework, ISO 31000 Risk Management Standard, and MAS’s risk management guidelines for financial institutions. Most Singapore organizations adopt COSO as their foundational framework while incorporating Singapore-specific regulatory requirements. Q6: Who should be responsible for enterprise risk management? Enterprise risk management is a shared responsibility. The Board provides governance oversight, the Chief Risk Officer or Risk Management function develops and implements the ERM framework, business units identify and manage operational risks, and all employees contribute through risk awareness. Effective ERM requires cross-functional collaboration and executive commitment. Conclusion: Building a Resilient Organization through Enterprise Risk Management Enterprise Risk Management Singapore represents an essential investment for organizations seeking to build resilient, well-governed businesses capable of navigating uncertainty while pursuing growth. By implementing comprehensive ERM frameworks aligned with COSO principles and Singapore regulatory requirements, organizations enhance decision-making, reduce losses, and demonstrate governance excellence to stakeholders. The question is no longer whether to implement enterprise risk management, but how quickly organizations can establish sophisticated risk management capabilities that create competitive advantage and stakeholder value.